{ "@context": "https://schema.org", "@graph": [ { "@type": "WebPage", "@id": "https://www.strike48.com/solutions/security/ai-threat-hunting#webpage", "url": "https://www.strike48.com/solutions/security/ai-threat-hunting", "name": "AI Threat Hunting Across Your Whole Stack", "description": "Strike48 threat hunter agents test hypotheses against every connected source, including cold storage, and turn validated findings into tested detections and tickets.", "inLanguage": "en", "isPartOf": { "@id": "https://www.strike48.com/#website" }, "about": { "@id": "https://www.strike48.com/solutions/security/ai-threat-hunting#software" }, "publisher": { "@id": "https://www.strike48.com/#organization" }, "breadcrumb": { "@id": "https://www.strike48.com/solutions/security/ai-threat-hunting#breadcrumb" } }, { "@type": "SoftwareApplication", "@id": "https://www.strike48.com/solutions/security/ai-threat-hunting#software", "name": "Strike48 AI Threat Hunting", "applicationCategory": "SecurityApplication", "operatingSystem": "Web", "description": "Threat hunter agents on the Strike48 agentic orchestration platform test hypotheses against every connected source and turn validated findings into tested detection rules and tickets. SaaS deploys the same day, with private cloud, on-premises and air-gapped options.", "featureList": [ "Hypothesis-driven threat hunting across every connected source", "Queries data in SIEMs, EDR, identity platforms, data lakes and cloud storage, including S3", "Pre-built Threat Hunter agent", "Prospector Studio no-code agent builder", "Coverage gap analysis against MITRE ATT&CK techniques", "Deterministic workflows with every step on the audit trail", "Validated findings converted into tested detection rules", "Native query translation for SPL, KQL and more", "Ticket creation in ServiceNow and Jira", "Timeline reconstruction back to patient zero" ], "publisher": { "@id": "https://www.strike48.com/#organization" } }, { "@type": "Organization", "@id": "https://www.strike48.com/#organization", "name": "Strike48", "url": "https://www.strike48.com", "logo": { "@type": "ImageObject", "url": "https://cdn.prod.website-files.com/69600380b333d9899a713351/69603d322ef6dcf90c3f988d_Strike48%20Logo_RGB_2C.svg" }, "sameAs": [ "https://www.linkedin.com/company/strike48/", "https://www.youtube.com/@Strike48-AI", "https://github.com/Strike48-public", "https://discord.com/invite/J3mukDFzfq" ] }, { "@type": "BreadcrumbList", "@id": "https://www.strike48.com/solutions/security/ai-threat-hunting#breadcrumb", "itemListElement": [ { "@type": "ListItem", "position": 1, "name": "Home", "item": "https://www.strike48.com/" }, { "@type": "ListItem", "position": 2, "name": "Security Solutions", "item": "https://www.strike48.com/solutions/security" }, { "@type": "ListItem", "position": 3, "name": "AI Threat Hunting", "item": "https://www.strike48.com/solutions/security/ai-threat-hunting" } ] } ] } { "@context": "https://schema.org", "@graph": [ { "@type": "WebPage", "@id": "https://www.strike48.com/solutions/security/ai-threat-hunting#webpage", "url": "https://www.strike48.com/solutions/security/ai-threat-hunting", "name": "AI Threat Hunting Across Your Whole Stack", "description": "Strike48 threat hunter agents test hypotheses against every connected source, including cold storage, and turn validated findings into tested detections and tickets.", "inLanguage": "en", "isPartOf": { "@id": "https://www.strike48.com/#website" }, "about": { "@id": "https://www.strike48.com/solutions/security/ai-threat-hunting#software" }, "publisher": { "@id": "https://www.strike48.com/#organization" }, "breadcrumb": { "@id": "https://www.strike48.com/solutions/security/ai-threat-hunting#breadcrumb" } }, { "@type": "SoftwareApplication", "@id": "https://www.strike48.com/solutions/security/ai-threat-hunting#software", "name": "Strike48 AI Threat Hunting", "applicationCategory": "SecurityApplication", "operatingSystem": "Web", "description": "Threat hunter agents on the Strike48 agentic orchestration platform test hypotheses against every connected source and turn validated findings into tested detection rules and tickets. SaaS deploys the same day, with private cloud, on-premises and air-gapped options.", "featureList": [ "Hypothesis-driven threat hunting across every connected source", "Queries data in SIEMs, EDR, identity platforms, data lakes and cloud storage, including S3", "Pre-built Threat Hunter agent", "Prospector Studio no-code agent builder", "Coverage gap analysis against MITRE ATT&CK techniques", "Deterministic workflows with every step on the audit trail", "Validated findings converted into tested detection rules", "Native query translation for SPL, KQL and more", "Ticket creation in ServiceNow and Jira", "Timeline reconstruction back to patient zero" ], "publisher": { "@id": "https://www.strike48.com/#organization" } }, { "@type": "Organization", "@id": "https://www.strike48.com/#organization", "name": "Strike48", "url": "https://www.strike48.com", "logo": { "@type": "ImageObject", "url": "https://cdn.prod.website-files.com/69600380b333d9899a713351/69603d322ef6dcf90c3f988d_Strike48%20Logo_RGB_2C.svg" }, "sameAs": [ "https://www.linkedin.com/company/strike48/", "https://www.youtube.com/@Strike48-AI", "https://github.com/Strike48-public", "https://discord.com/invite/J3mukDFzfq" ] }, { "@type": "BreadcrumbList", "@id": "https://www.strike48.com/solutions/security/ai-threat-hunting#breadcrumb", "itemListElement": [ { "@type": "ListItem", "position": 1, "name": "Home", "item": "https://www.strike48.com/" }, { "@type": "ListItem", "position": 2, "name": "Security Solutions", "item": "https://www.strike48.com/solutions/security" }, { "@type": "ListItem", "position": 3, "name": "AI Threat Hunting", "item": "https://www.strike48.com/solutions/security/ai-threat-hunting" } ] } ] }
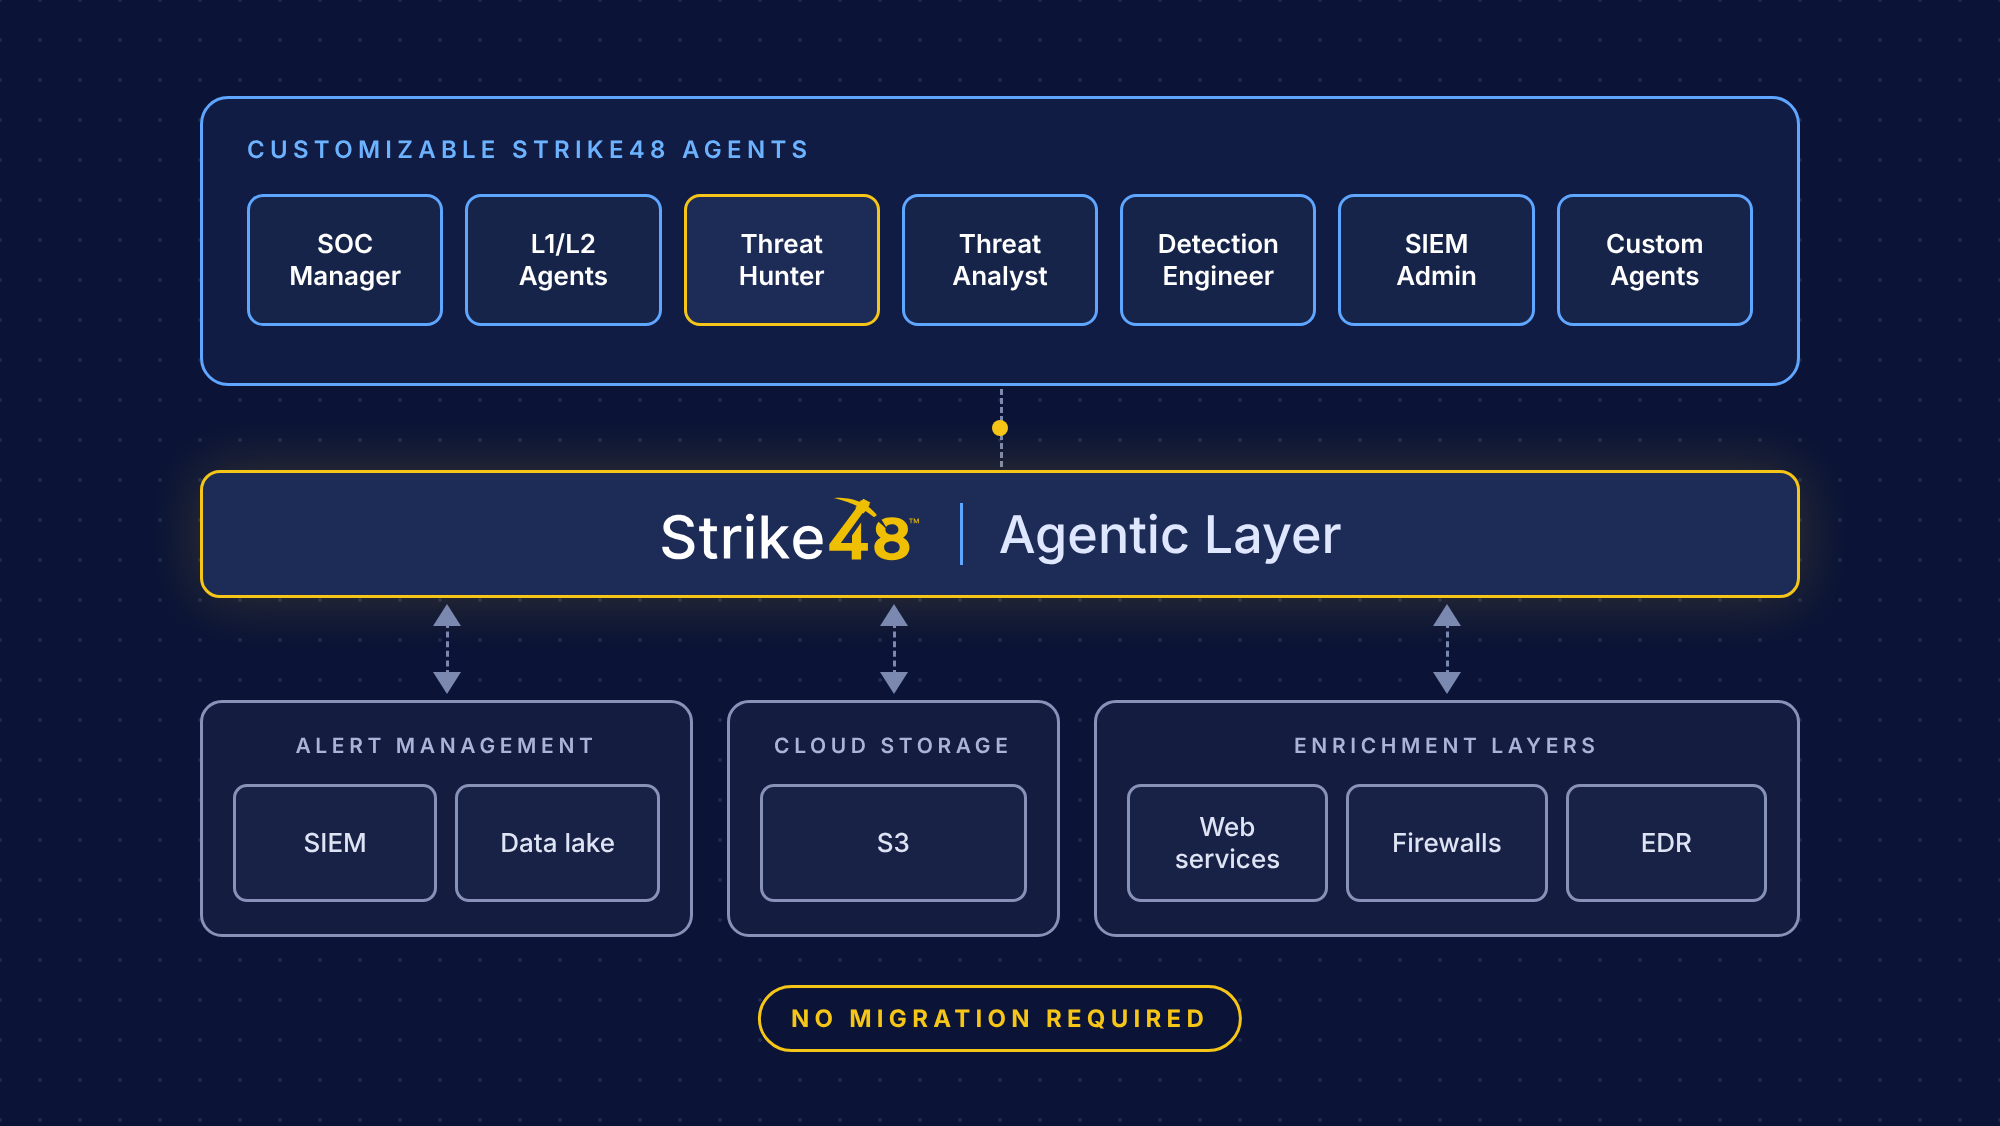
Strike48 threat hunter agents work across your environment. Start with the pre-built agent and customize your processes. You decide which actions run on their own.
HUNT THreats WITH AI
Most hunts start with partial data and end in a notes file. Strike48 connects to your existing stack, so agents test a hypothesis against every connected source and carry what they find into detections and tickets. Analysts write the hypothesis in plain language. Workflows run the same steps the same way on every hunt, so results hold up to review.

Agents query data where it lives, whether you run one SIEM, several, or none. Logs in S3 and other low-cost storage stay reachable without a second copy or a move to a hot tier. Ask "are we exposed?" once and get an answer drawn from every connected source.
The pre-built Threat Hunter agent runs hypothesis-driven hunts from day one. In Prospector Studio, the no-code builder, analysts write hypotheses in plain language and build hunt agents scoped to their own environment. Coverage gap analysis shows which MITRE ATT&CK techniques have no detection behind them.


Strike48 workflows run deterministic steps wherever they can and call the model only at bounded points. The same facts produce the same answer on every run, and every step lands on the audit trail. Agents are grounded in your runbooks and case history, so each conclusion points back to telemetry from your environment.
When a hunt finds activity, the L2 agent reconstructs the timeline back to patient zero and maps it to MITRE ATT&CK. Validated findings become detection rules, tested before they go live, and tickets in ServiceNow or Jira. Containment and remediation wait for analyst approval unless you choose otherwise.

integrations
Strike48 connects to SIEMs, EDR, identity platforms, email security, network tools, data lakes and cloud storage. Native query translation covers SPL, KQL and more, so nobody has to learn each tool's query language to hunt in it. Analysts stop pivoting between consoles. Agents correlate evidence across sources and hand back one answer, with no migration and no change to existing processes.
Results from Strike48 customers in a 7-day period.
benefits
Check a new CVE against your software versions and open ports without waiting for scanner plugins.
Reach the data your detections never touched, including logs in cold storage.
Analysts hunt in plain language instead of learning each tool's query syntax.
Validated hunts turn into tested detection rules, not notes in a shared drive.
getting started
SaaS deploys the same day. Private cloud, on-premises and air-gapped options are available.
Grant read-only access to your SIEMs, EDR, identity logs, storage, and any other sources you want to hunt.
Sync runbooks, past cases and TTP profiles so agents work from how your environment actually runs.
Run the Threat Hunter agent, or write your own custom hunter in Prospector Studio.
Strike48 is the agentic orchestration platform for security and IT. Bring a hypothesis and watch the Threat Hunter agent test it against your stack.