
Strike48's on-prem SOC appliance provides the first turnkey deployment of agentic security operations capabilities for air-gapped environments. Choose your models and your telemetry never leaves.
Run the full agentic platform on a server with no external connection. Classified, sovereign, and isolated environments get the same autonomous capabilities as cloud deployments.
Security telemetry stays on-site or in-country. Organizations under residency mandates or cloud prohibitions can adopt agentic operations without moving a single log.
Models are loaded onto the appliance and run inside encrypted memory. Prompts, telemetry, and context stay protected, so there is no path for cross-pollination into an externally hosted model.
Local inference removes per-token billing from the equation. The appliance scales at a fraction of the cost of a SaaS deployment, which makes expansion a budget decision you can actually model.
Strike48 can run in the cloud, managed or in a private cloud you control, or on-premises on an appliance, with the option to be fully air-gapped with no external connection.
The platform, the agents, and the operator experience stay identical across all four. You choose the modality that matches your regulatory posture and change it as that posture changes.
| Managed cloud (SaaS) | On-premises appliance | |
|---|---|---|
| Where it runs | Strike48's AWS account | Your hardware, with no dependency on Strike48's cloud |
| Edge | Cloudflare fronts all traffic and absorbs DDoS and WAF duties | N/A |
| Identity | Keycloak as OIDC identity provider at the edge | Identity service runs on the appliance |
| In transit | TLS 1.3 browser to edge and edge to origin, AES-256-GCM inside the boundary on the AWS Nitro System | TLS at the single entry point, encrypted memory space between services |
| At rest | Amazon RDS encrypted with AWS KMS | You control the encryption or trusted hardware level |
| Orchestration | Private Kubernetes cluster with horizontally scaling worker nodes | You control the encryption or trusted hardware level |
| Inference | Hosted model access | Optional on-appliance inference layer with local GPU |
| Deployment modalities | Cloud Private Cloud | On-Premises On-Prem / Air-Gapped |
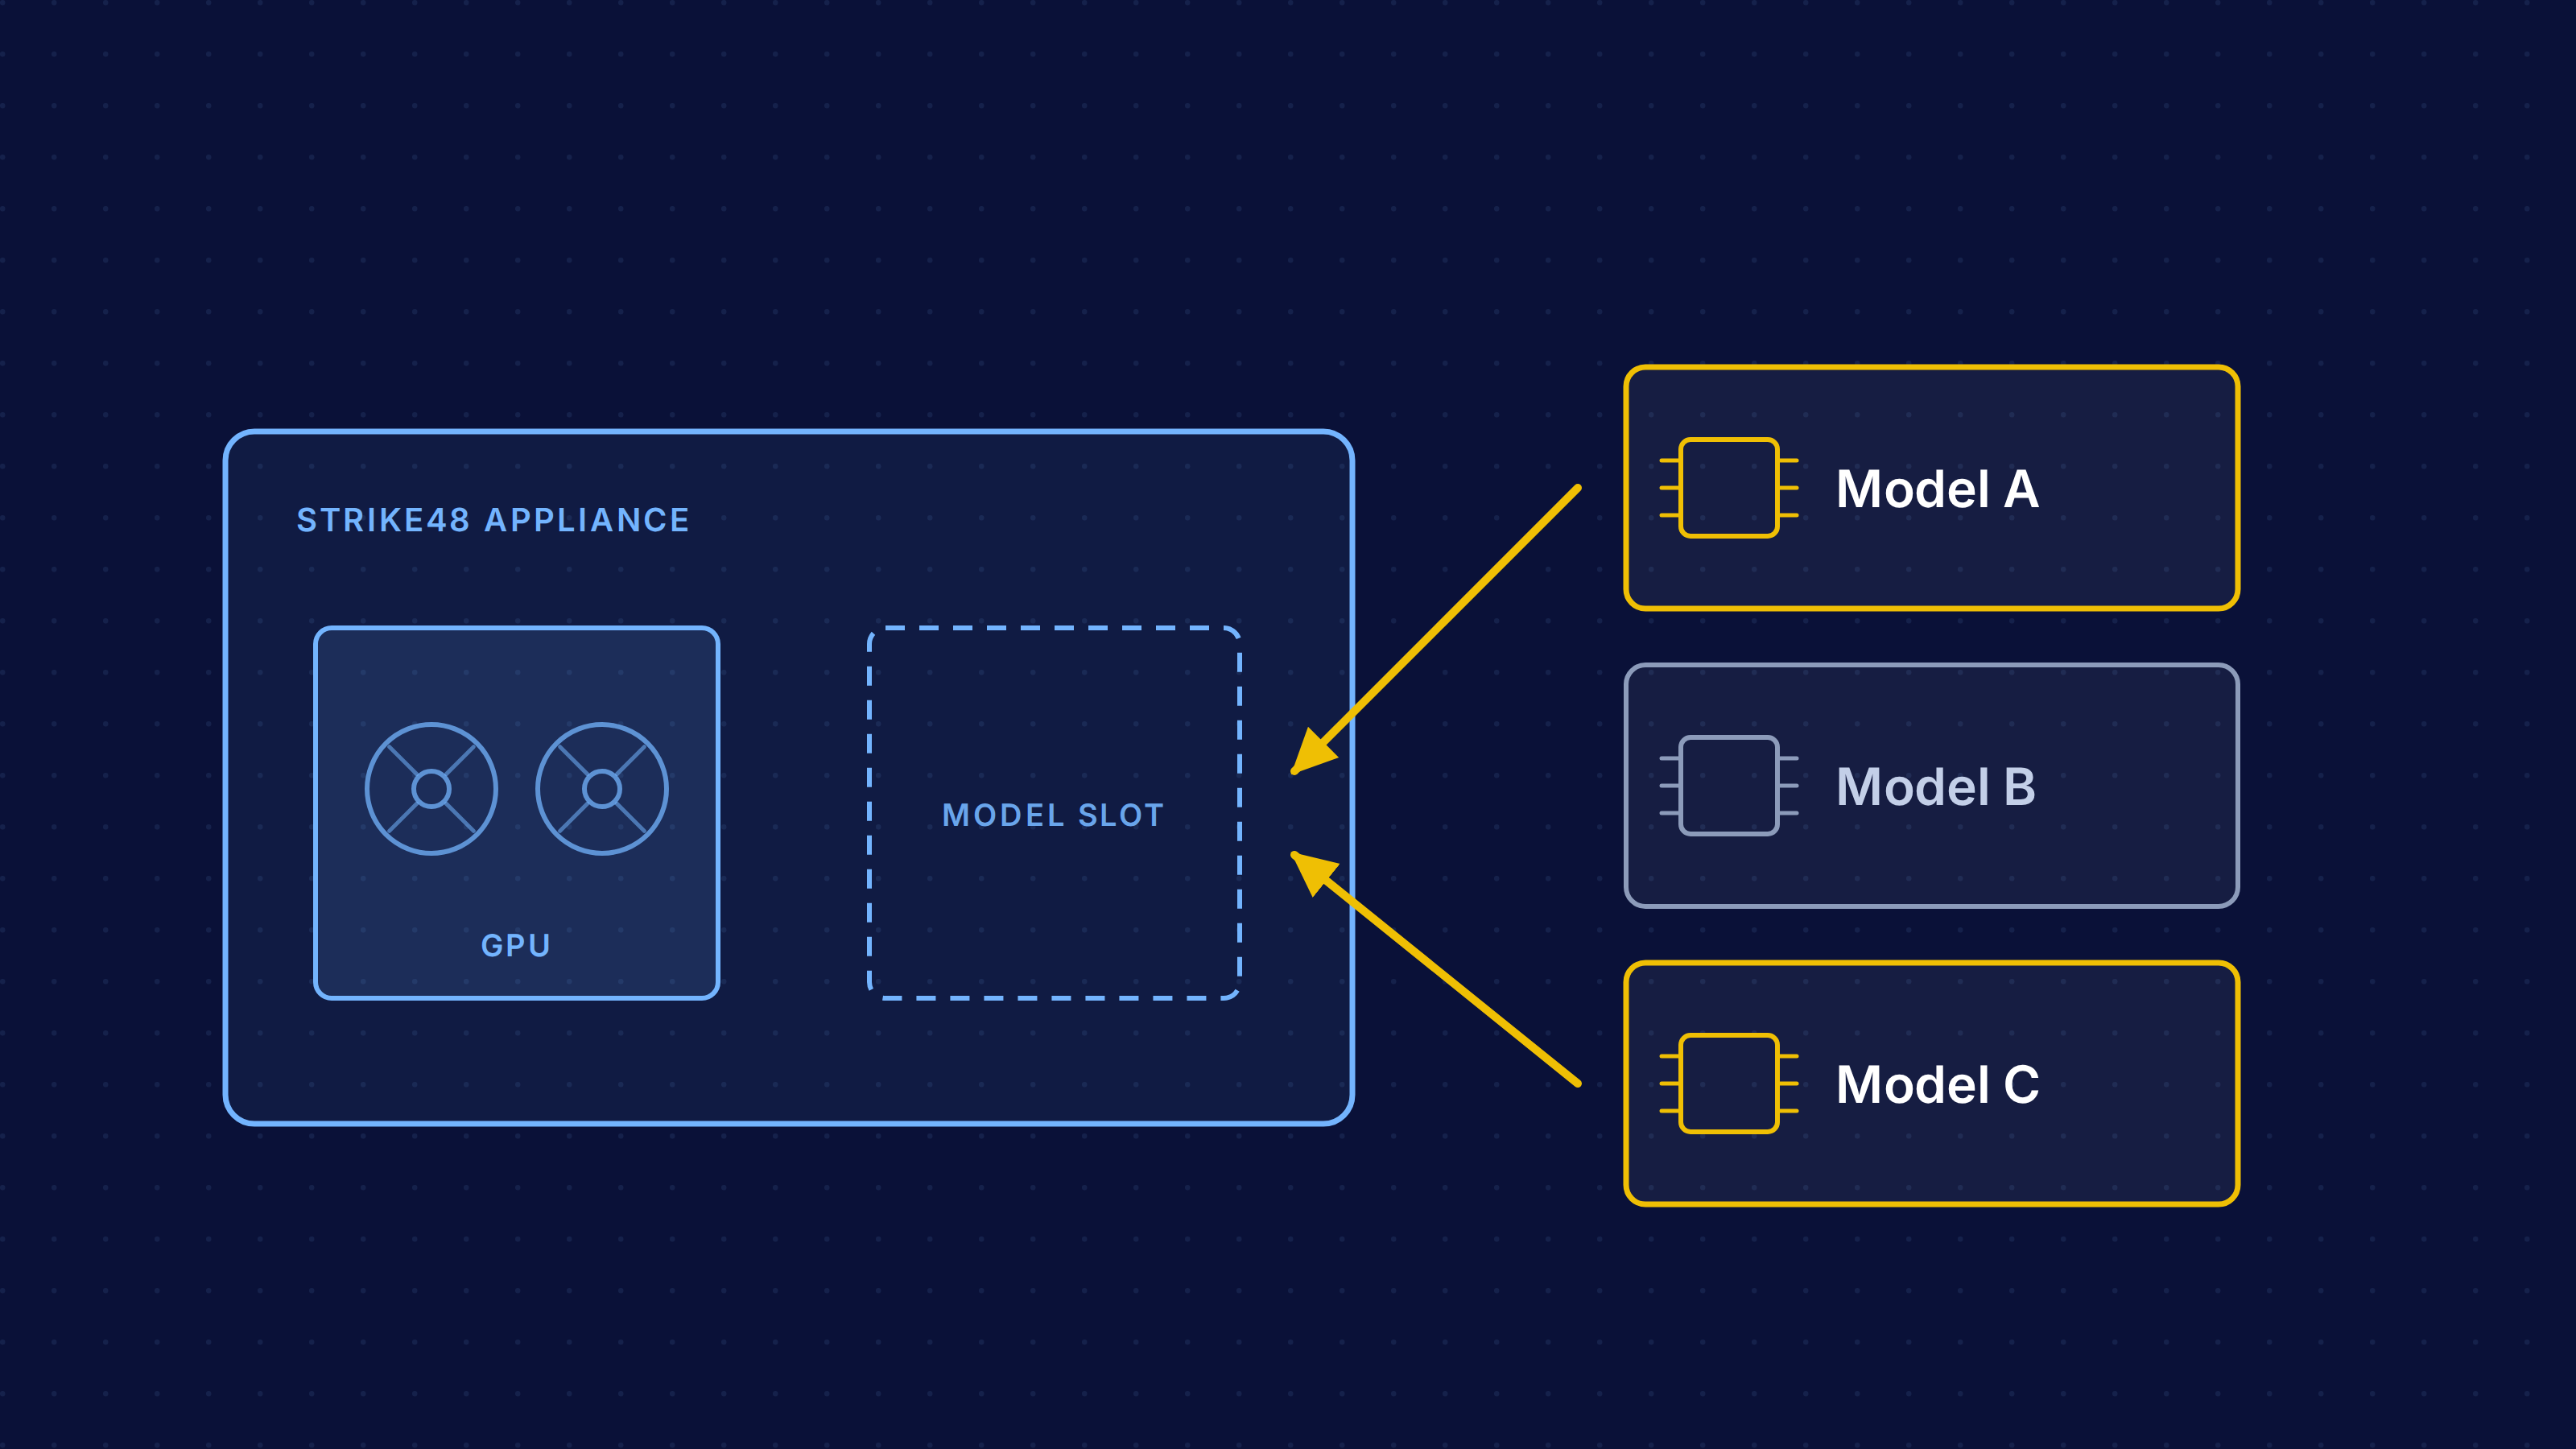
For on-premises and air-gapped deployments, an inference layer is added to the appliance and AI models are loaded directly onto it. A GPU attaches through PCI passthrough with CUDA, so model execution happens entirely on your hardware and the platform makes no external API calls. Model flexibility was built into Strike48 from the start, so we package models that are approved for your controlled environment rather than binding you to one model developer. When a better model arrives, you swap it. The agents keep running.
Most agentic tools degrade when you cut them off from frontier model updates. Strike48 splits work between deterministic agents that execute defined procedures and cognitive agents that reason over context. That architecture supports a fully enclosed system that holds its quality without relying on broader LLM learning loops. Detection engineering, alert triage, phishing investigation, and threat hunting all run inside the perimeter.

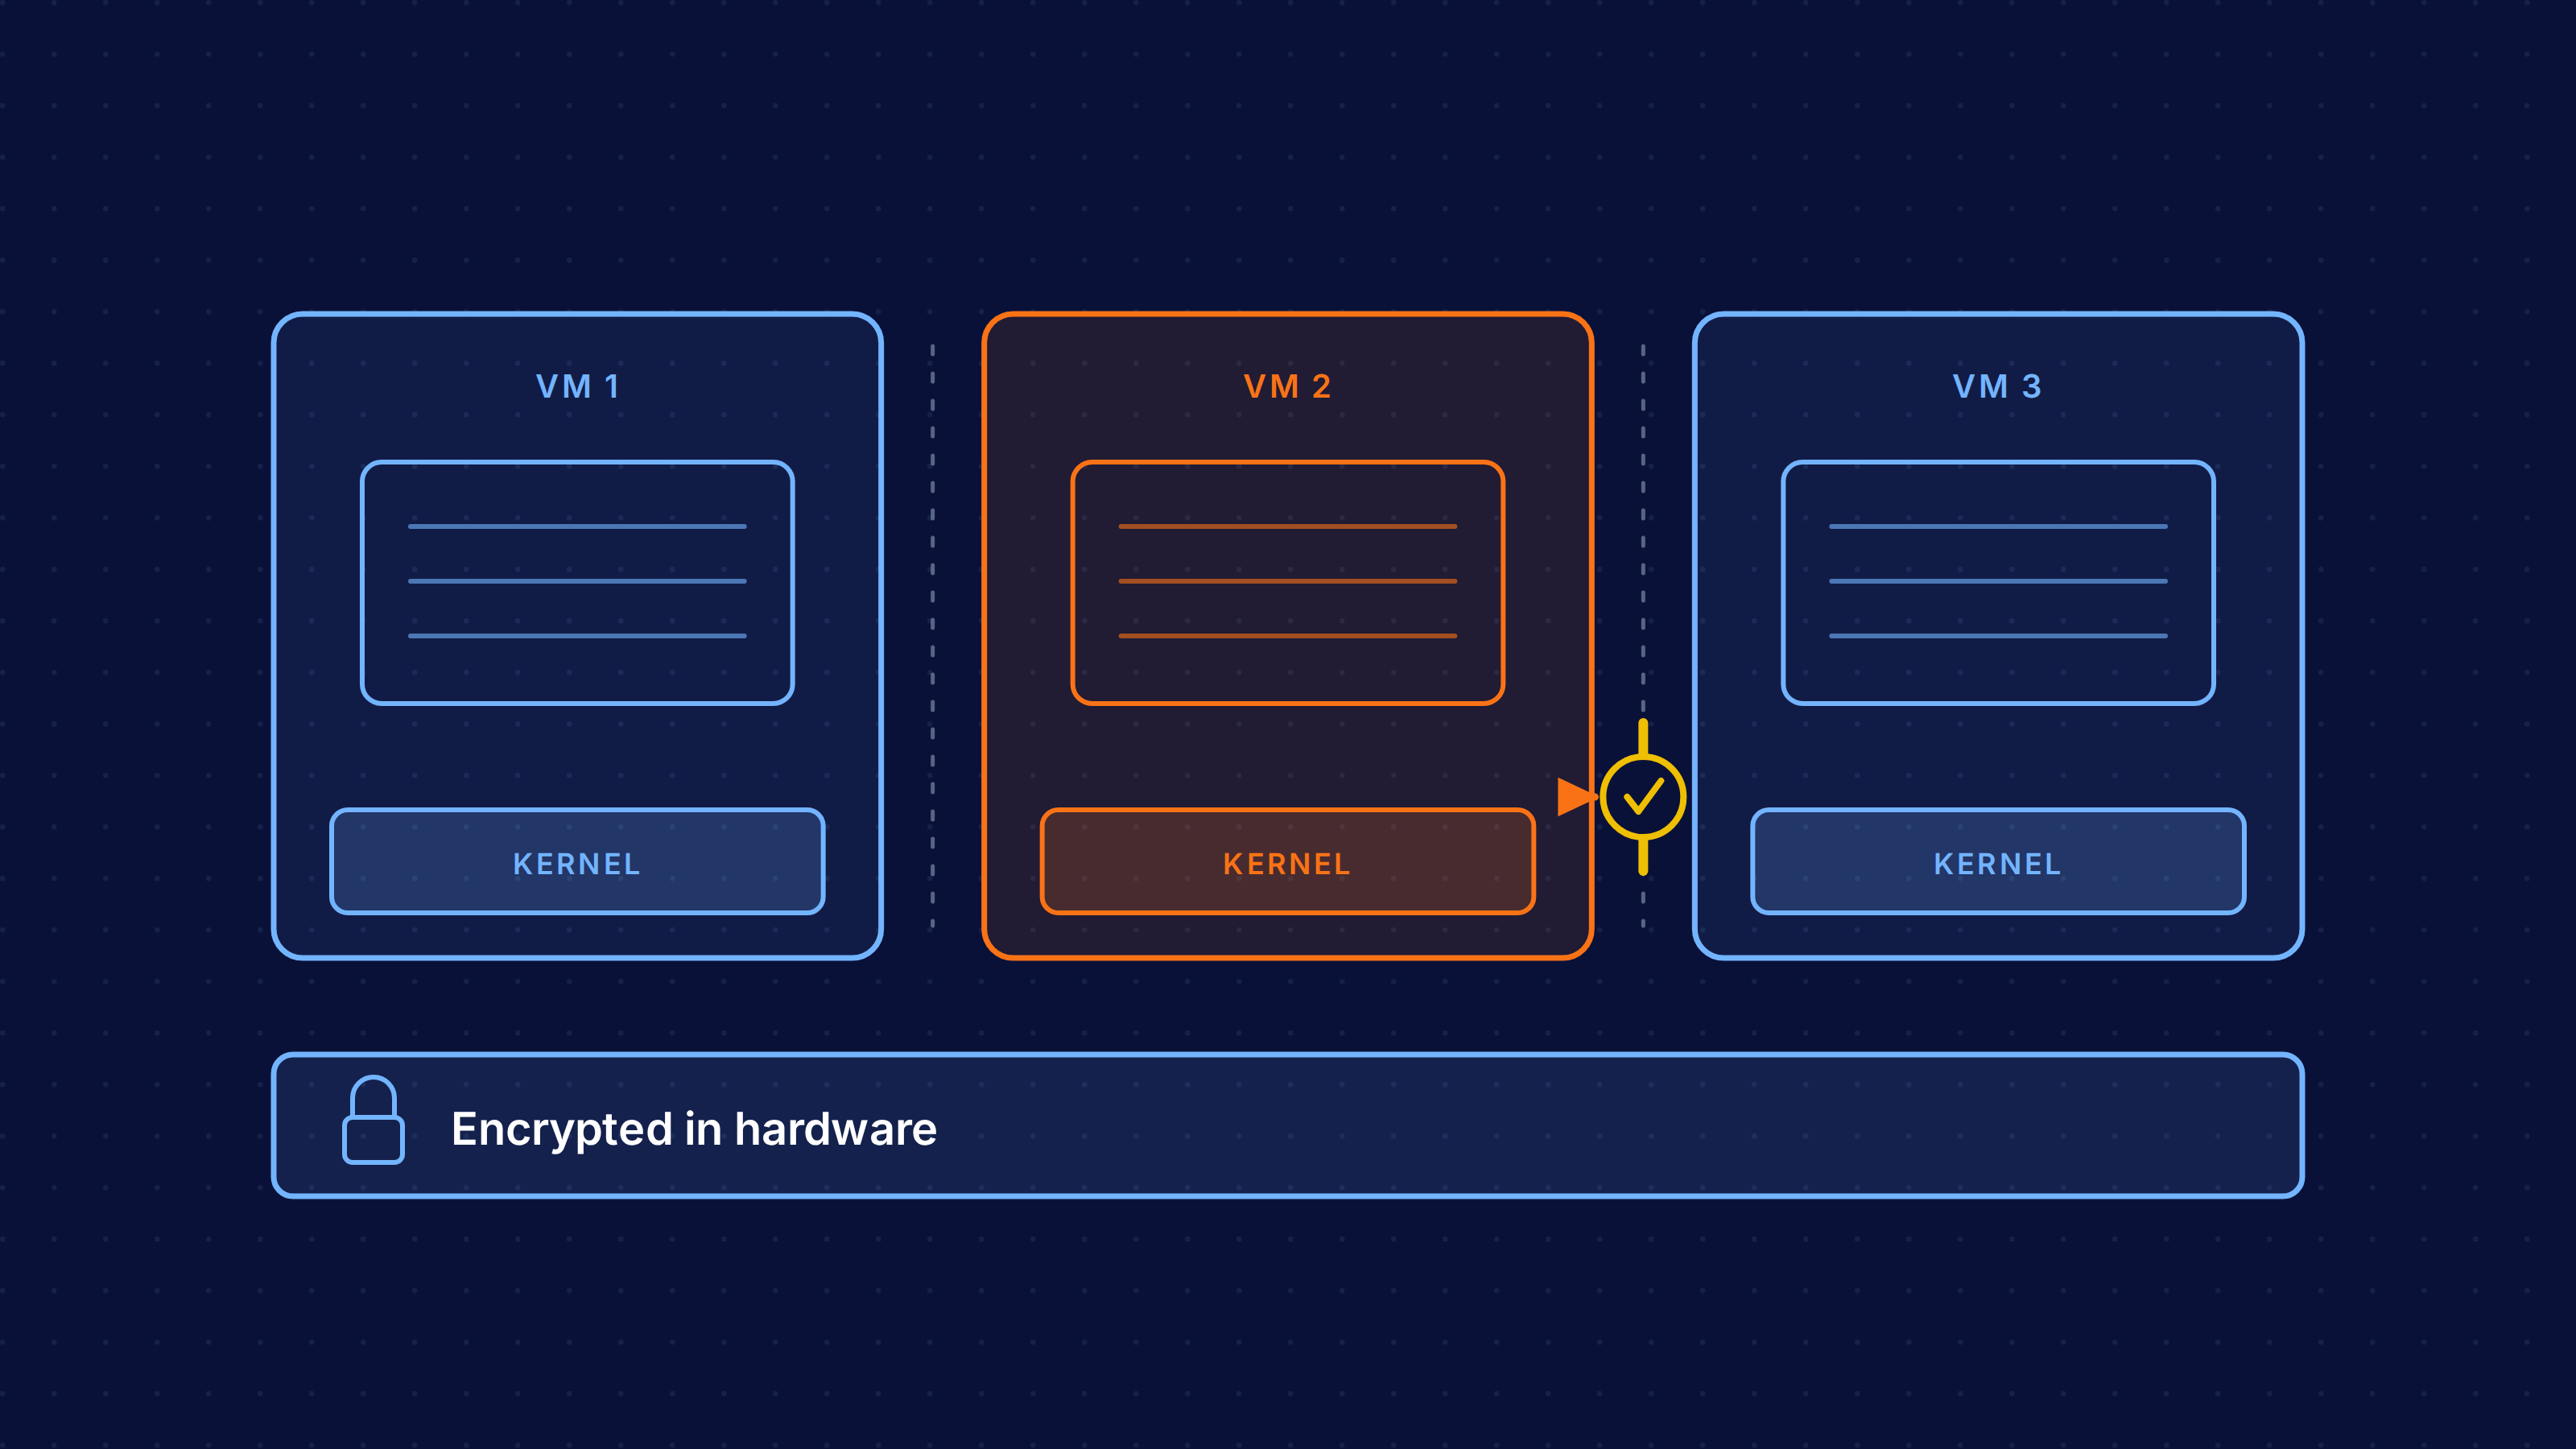
The appliance runs on trusted compute, which means CPU memory encryption protects workload memory from the host it runs on. Every workload runs as a pod inside its own lightweight virtual machine with a dedicated guest kernel, separated by network policy. A compromise in one service cannot reach another through a shared kernel, and communication between virtual machines stays inside encrypted memory space. Isolation is enforced by the hardware rather than by configuration you have to maintain.
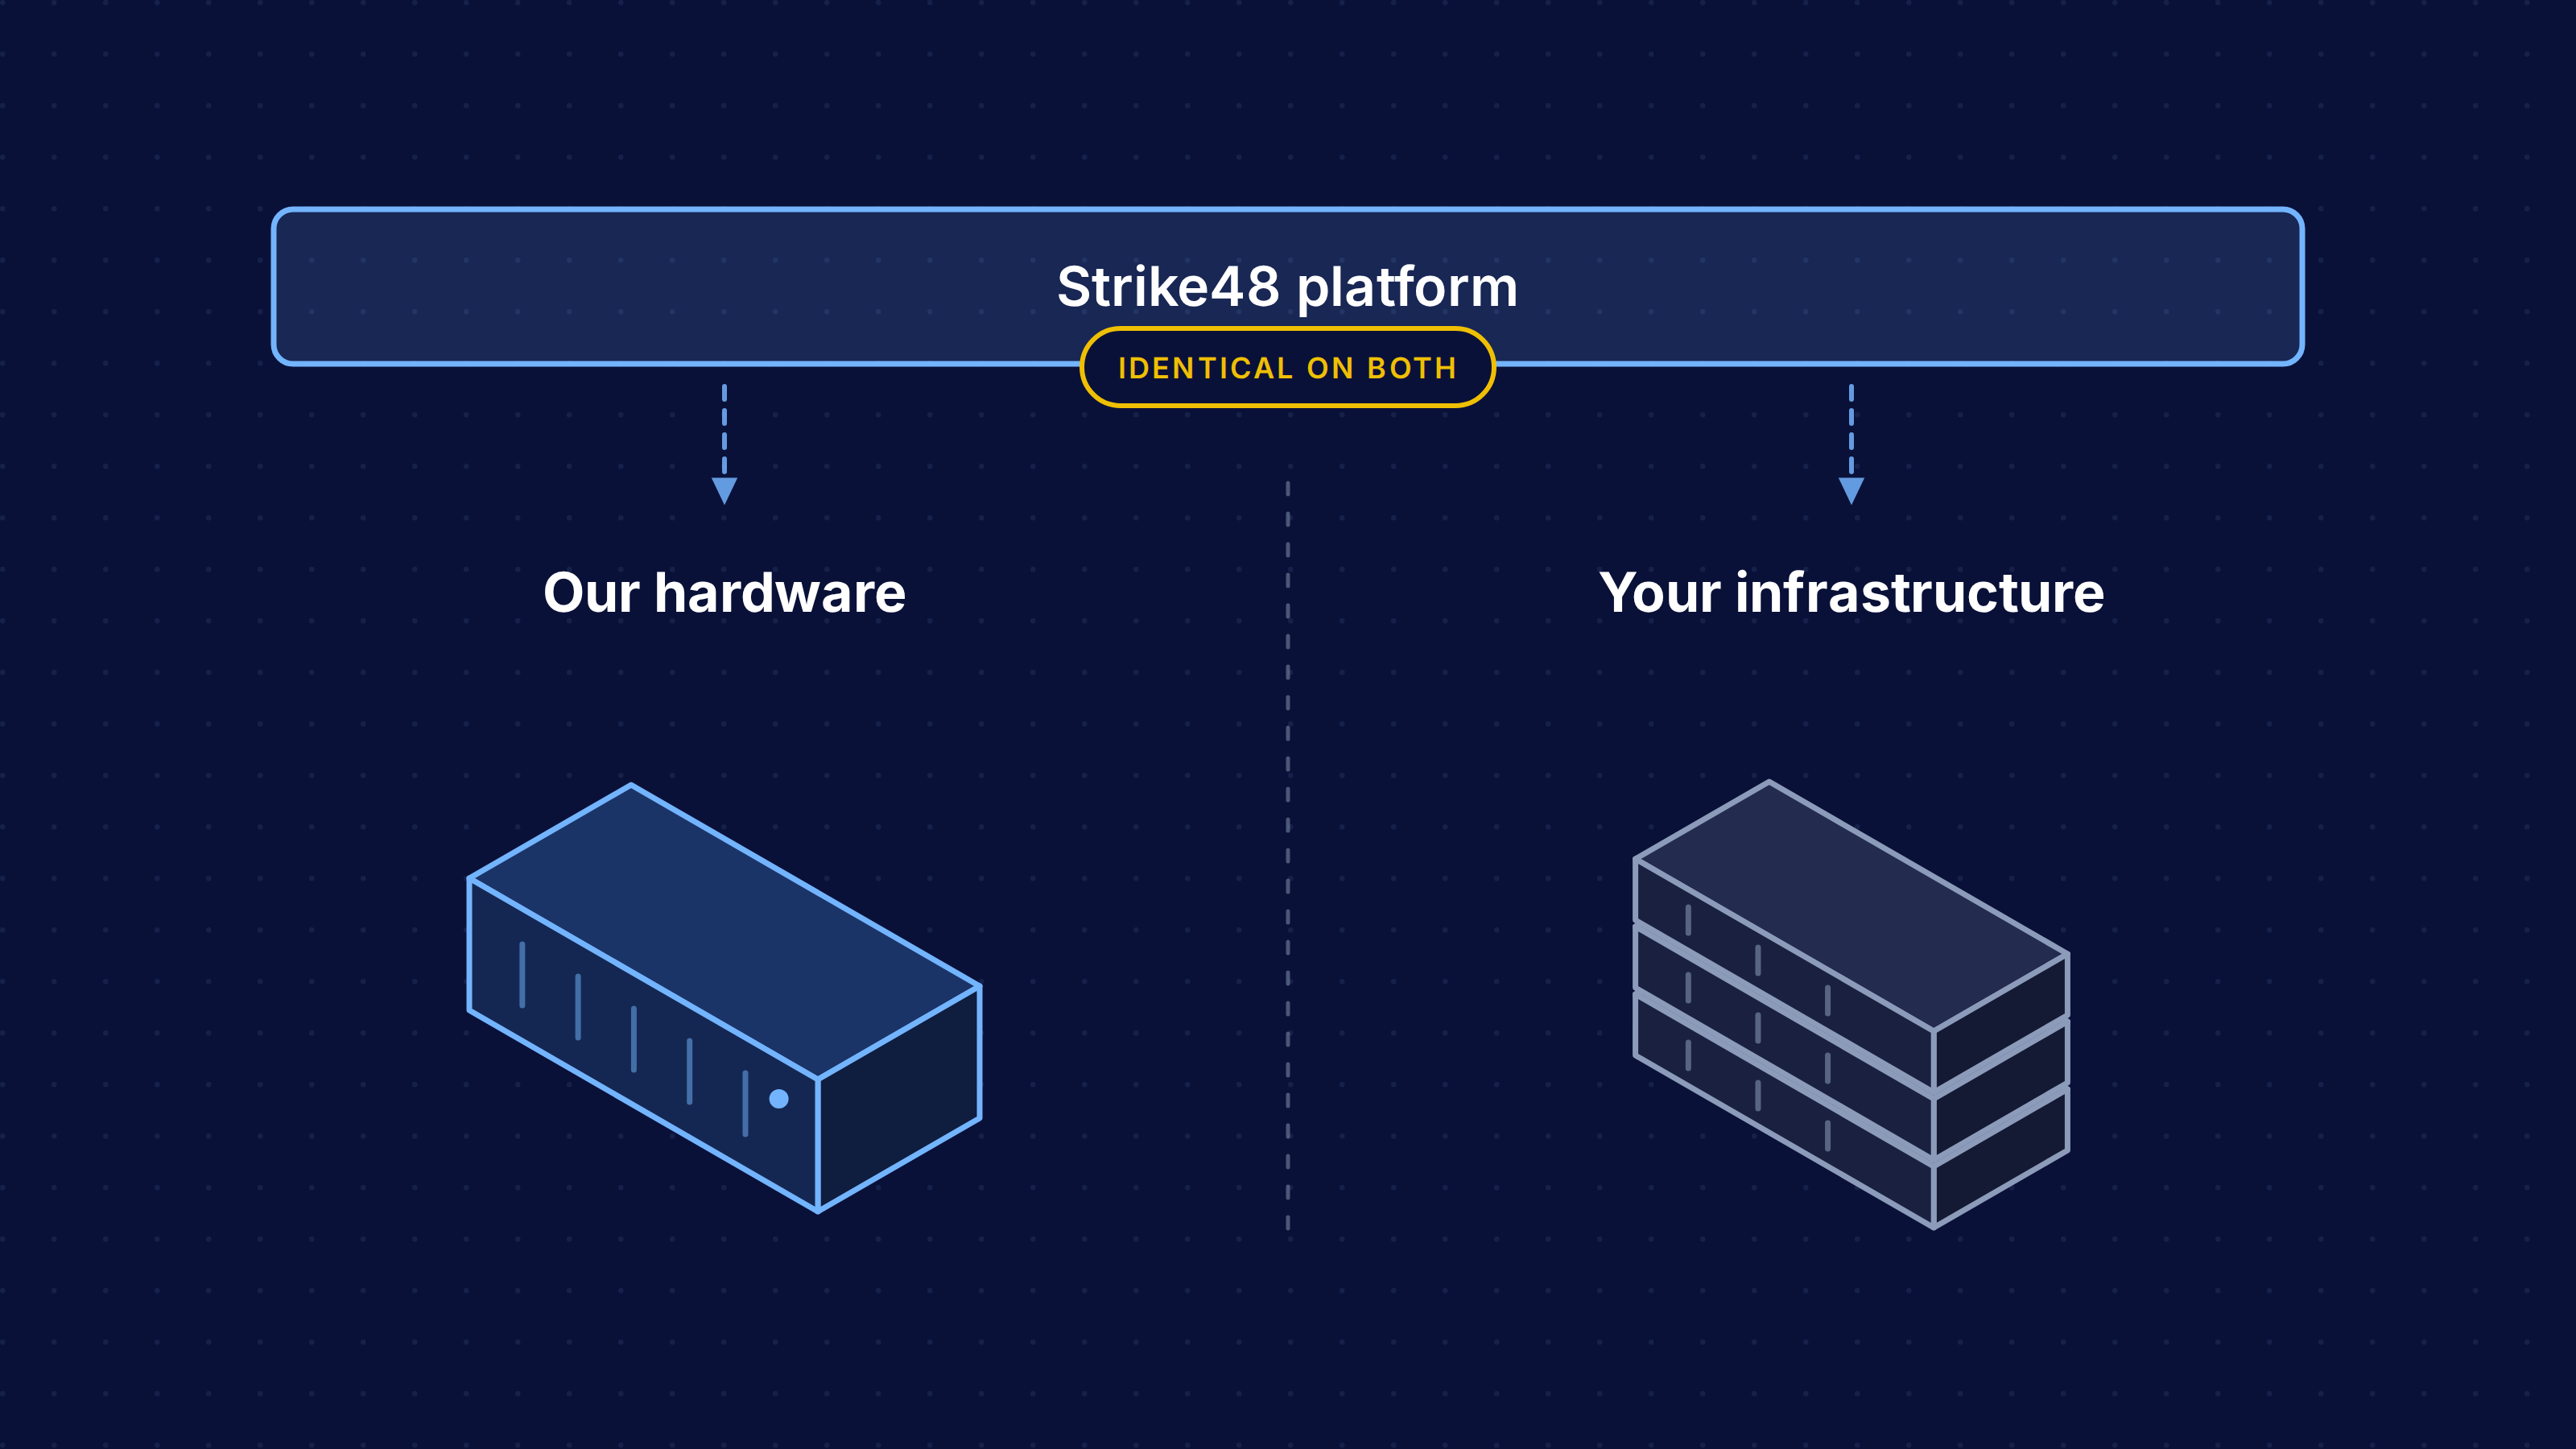
The Strike48 Appliance ships as dedicated hardware or as a soft-appliance on infrastructure that meets our specifications. Kubernetes orchestrates the platform at the system level in both cases, so the deployment model changes who owns the metal and nothing else. Existing investments stay in place. Strike48 works across your environment without requiring you to centralize data or replace the tooling you already run.
Requirements
Trusted compute.
CPU memory encryption, so workload memory is protected from the host.
Disk encryption.
Full-disk encryption supplied to the operating system.
Single SSL termination.
One TLS endpoint for all external traffic.
Orchestration.
You control the encryption or trusted hardware level.
Hardware-level isolation per service.
Pods in dedicated virtual machines with network-policy separation.
Optional local inference.
An LLM inferencing layer with a GPU attached via PCI passthrough.
For Service Providers
A share of every MSSP pipeline sits blocked on cloud AI adoption. Regulatory limits, data residency rules, and internal security policy keep those accounts on legacy service models. The Appliance turns that segment into addressable revenue, delivered inside the customer environment and managed as part of your service.
Autonomous enrichment and disposition
End-to-end analysis and verdict
Rule creation and tuning
Hypothesis-driven investigation
Governed action with approval gates
Query across sources without centralizing
Get a walkthrough of the Strike48 Appliance and see how on-premises and air-gapped deployments change what your team can automate.
